Security & Compliance

The best audit is the one that doesn’t reveal anything new to you. We prepared the critical infrastructure of one of Europe’s largest port operators for a BSI IT-Grundschutz audit in three months. We implemented controls across multiple data centers, multiple cloud providers, the Kubernetes platform, and the applications running on it.

The challenging part of compliance lies beneath your application. We build the controlled foundation, implement the controls on top of it, and keep the evidence up to date—so you can export documentation instead of having to compile it.

TRUSTED BY TEAMS AT:

  • Deutsche Telekom logo: white stylised letter T on a magenta background
  • Uniper logo in blue, showing the word "uniper" split across two lines.
  • GOLDBECK logo in bold black uppercase letters on a white background
  • PwC logo featuring the lowercase letters "pwc" in black with two orange diagonal shapes above
  • Vattenfall logo with the name in dark grey bold letters and a circle split into yellow upper half and blue lower half on the right
  • Schwarz-produktion logo on a white background reading “SCHWARZ PRODUKTION” in white text inside a dark blue square.
  • Cornelsen logo — white bold wordmark on a red background
  • Meridiam logo with tagline "for people and the planet" in dark green on a white background.

What exactly is Cloud Security & Compliance?

BSI IT-Grundschutz, NIS2, DORA, GDPR, or CRA describe what must be met—but the real challenge lies in ensuring that these requirements remain in place even as applications, infrastructure, providers, and requirements are constantly changing.

When implemented correctly, compliance goes far beyond merely meeting auditor requirements: It provides you with transparency and control over your assets, data, access, changes, and dependencies—and turns security requirements into something your teams can actually implement in their day-to-day operations.

Compliance permeates every layer

Your application can only be as secure and compliant as the layers beneath it. We build on a robust cloud infrastructure, add platform controls on top of it, and integrate your applications into this foundation. You focus on what’s specific to your application; we take care of the controls beneath it.
Two colleagues working together at a wooden table near a window, focusing on a laptop while a person walks by outside.

Audits should confirm reality, not create it

If proving a control means collecting screenshots, spreadsheets, and tickets from five teams, something is wrong. We keep control statuses, exceptions, and evidence linked to the running platform, so the work is already done when an auditor asks.

Team members seated at long wooden tables in a well-lit room, listening attentively to a presentation with open laptops and notebooks.

Sovereignty is more than just data storage

Knowing where your data is stored is just the beginning. Sovereignty means knowing who controls it, which software and services you depend on, and what a switch would actually cost—including egress costs, platform components that need to be rebuilt, and time.

We make portability, transparency regarding dependencies, and exit readiness part of governance—as long as these issues can still be resolved cost-effectively.

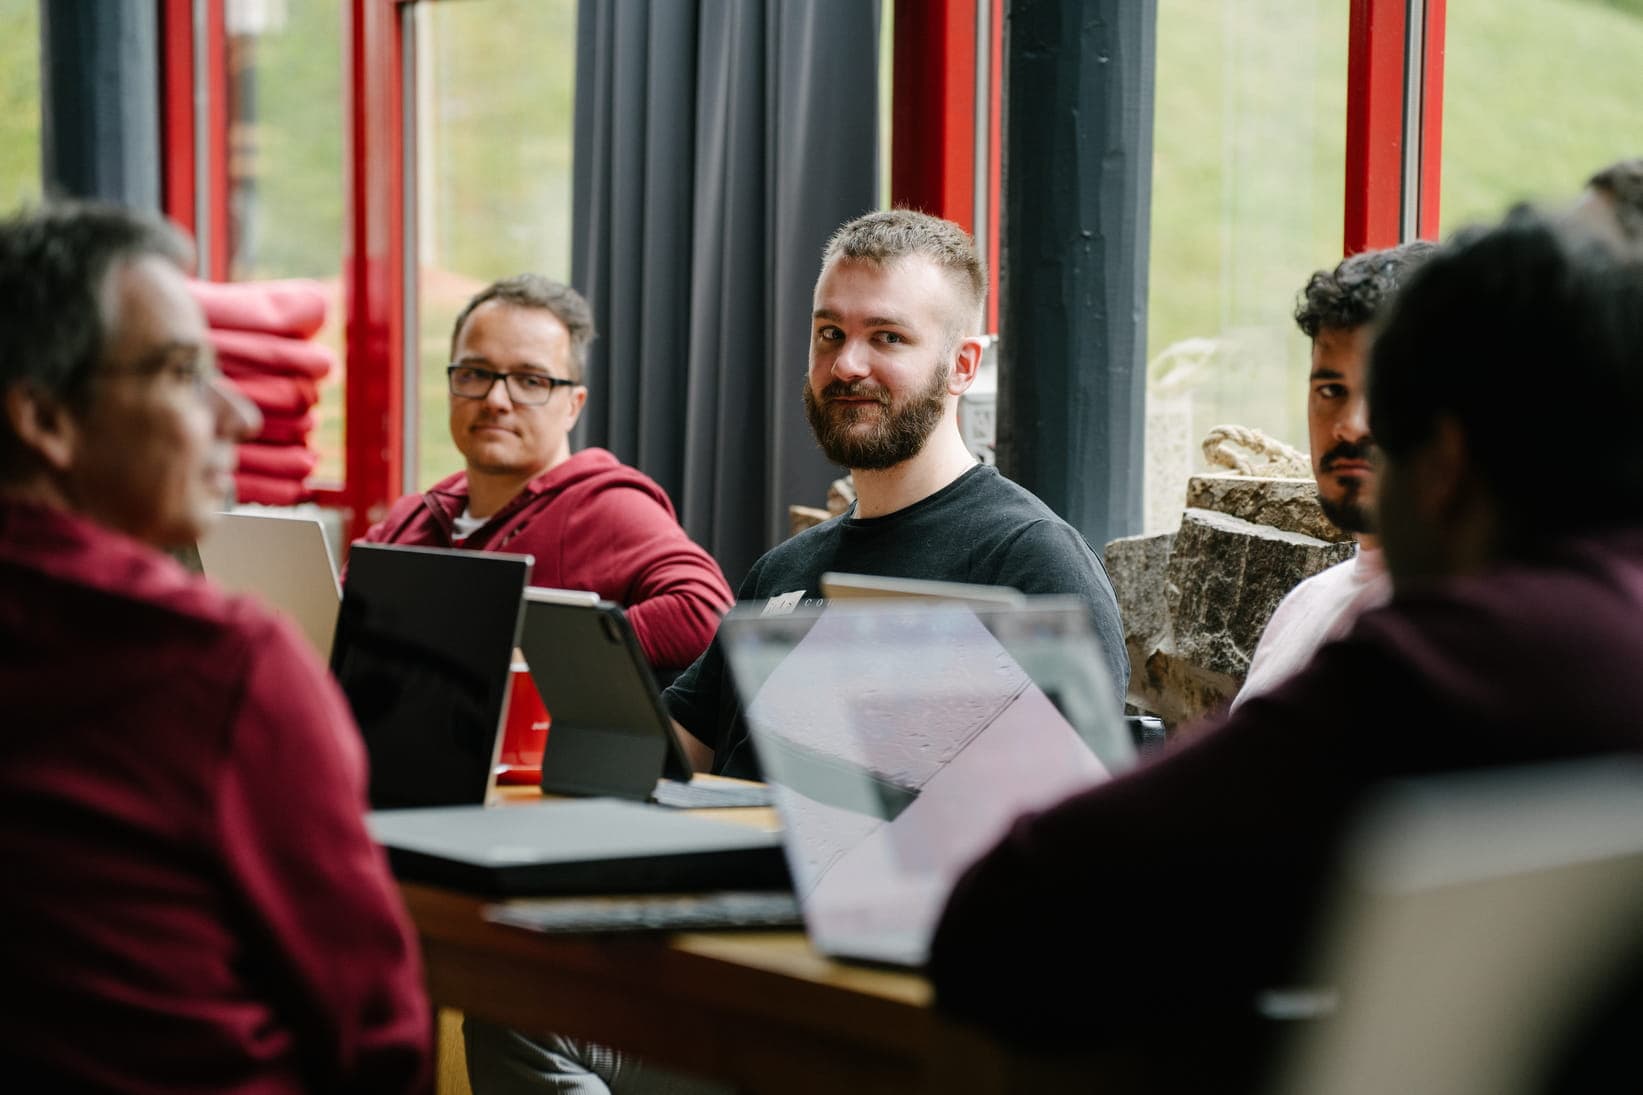
A group of men sitting around a table with laptops, participating in a meeting or workshop. One man with a beard and a black t-shirt smiles at the camera, while others look on.

Why This Will Pass the Audit

Send Inquiry
  • Regulated environments are familiar territorySeven years in regulated industries, including critical infrastructure, telecommunications, healthcare, the public sector, and financial services—with experience in audit preparation for one of Europe’s largest port operators.
  • We put our recommendations into practiceSecurity, Cloud Architecture, Platform Engineering, and CloudOps work together to ensure that requirements don’t end with an assessment. We translate them into identity controls, policies, guardrails, observability, and operational processes—and can then continue to manage them.
  • Compliance starts below the platformT Cloud Public and STACKIT provide us with a robust infrastructure foundation where needed. We build platform controls on top of that so your applications don’t have to reinvent identity, policy, logging, and governance from scratch every time. Open Standards Instead of Hidden Dependencies
  • Open Standards Instead of Hidden DependenciesOur platforms rely heavily on widely adopted open-source and cloud-native technologies, including ecosystems managed by organizations such as the CNCF and the Linux Foundation. This gives us greater transparency into the software supply chain and reduces unnecessary dependencies on proprietary services.
  • Compliance That Lasts Beyond Go-LiveThrough KumoOps, our managed CloudOps service, controls, monitoring, and operational baselines remain an integral part of the running platform.

Four Steps. Understand. Build. Validate.

  1. Step 01

    Determine what applies

    Your industry, applications, data, providers, and regulatory scope. We map requirements to your actual architecture and identify the relevant gaps.

  2. STEP 02

    Implement

    Identity, encryption, network policies, logging, and guardrails become technical controls within the platform. No more PDFs describing what should happen.

  3. STEP 03

    Maintain

    Configurations change. Applications change. Regulations change. We continuously track controls, exceptions, and evidence to ensure compliance doesn’t lapse after the project ends.

  4. STEP 04

    Export Evidence

    See what’s been implemented, close gaps, and provide evidence when auditors or third parties ask—without turning every audit into a new project.

CGM logo — a dark blue sphere with white lettering and a grey arc — centered on a light and dark blue wave-pattern background.
CASE STUDY · HEALTHCARE

A BSI C5 Compliant Cloud for Healthcare Patient Portals

Complete redesign and migration of the healthcare infrastructure to the T Cloud Public with BSI C5-compliant security, including client isolation and complex integration of hospital networks.

Industries we support in

Critical Infrastructure

Security controls, compliance, and sovereignty for environments where availability and resilience are non-negotiable.

Financial Services

Operational resilience, traceability, third-party dependencies, and technical controls related to requirements such as DORA.

Public Sector

Sovereign infrastructure, controlled data access, and verifiable governance in cloud and platform environments.

Healthcare

Protected workloads, strong identity management, and tenant isolation with security and compliance at every level of the infrastructure.

iits‑consulting’s ability to develop a complex and secure cloud environment under tight deadlines while meeting the highest technical and security requirements has made it a valuable partner. I recommend iits‑consulting for challenging IT projects, particularly in areas that require a high level of security and technical excellence.
CompuGroup Medical logo featuring a dark blue sphere with "CGM" in white letters and the text "CompuGroup Medical" to its right.Patrice Brend'amourVice President of Development · CompuGroup Medical SE & Co. KGaA

What we build with.

Our Terraform modules and Helm charts are publicly available. The controls listed below are not a comprehensive list of features—you can review them on GitHub before contacting us.

CONTROLS & GUARDRAILS
  • Kyverno Admission Policies
  • Keycloak
  • OIDC & SAML SSO
  • Cert-Manager
  • KMS-verschlüsselter Speicher
  • VPC & Subnetz-Firewalls
DOCUMENTATION & QUALITY ASSURANCE
  • Cloud Trace Service
  • Policy Reporter
  • Prometheus
  • Grafana
  • Alertmanager
  • Elastic & Elastic Alert
SOVEREIGNTY & SUPPLY CHAIN
  • Cosign image signin
  • Registry allowlists
  • Terraform
  • Grype
  • Argo CD
  • T Cloud Public
  • STACKIT

Would your platform pass the audit or just your documentation?

Find out what you can demonstrate today, where controls still exist only on paper, and what it will take to close the gap.